AI finds every vulnerability. Seal fixes them first.
Attackers use AI to turn a published security fix into a working exploit in minutes. Seal takes the upstream fix as soon as it lands and backports it into the exact versions you run, before the CVE lands in your scanner. No migration, no code changes, no engineering time.


Why security and engineering teams trust us
It was the most smooth onboarding experience we have had. In the short amount of time, we were actually able to start seeing value from Seal Security. I can maintain the same version of my library, but do it in a way that's vulnerability free. It makes it a lot better from a security and developer experience because it's no longer battling prioritization. It's just a matter of: can Seal fix it? Yeah, absolutely.

Thanks to Seal’s product, we swiftly addressed security vulnerabilities and updated outdated code packages, saving us valuable time, which we estimated by months of engineering work.
Seal Security's solution has been transformative in helping us secure our open source dependencies. It empowers our security teams with standalone patches, enabling prompt resolution of critical and high security issues. Implementing this solution has been instrumental in maintaining FedRAMP compliance. Their approach has allowed us to handle vulnerabilities associated with CentOS EoL packages, and reinforce our existing protections.

Security enabled us to eliminate a major ongoing risk to our development roadmap. The integration with their solution was simple, allowing us to quickly achieve significant patching coverage and ensure the seamless remediation of vulnerabilities.
AI changed how vulnerabilities are found and exploited. Remediation didn't change.
high- and critical-severity vulnerabilities found with a single AI model, Claude Mythos Preview, in about a month.
Source: Anthropic, Project Glasswing update, May 22, 2026known exploited vulnerabilities in the first half of 2026 was exploited on or before the day its CVE was published (23.4%).
Source: VulnCheck, 1H 2026 State of Exploitation, July 2026of organizations carry security debt, and flaws are now created faster than teams can fix them.
Source: Veracode, 2026 State of Software Securityof CVEs have a public fix commit before the advisory, a median of 11 days earlier.
Source: Seal Security Research, The Silent Patch Gap (2026)Seal closes the gap: verified fixes for the versions you run, without upgrades, before the CVE.
"Progress on software security used to be limited by how quickly we could find new vulnerabilities. Now it's limited by how quickly we can verify, disclose, and patch the large numbers of vulnerabilities found by AI."Anthropic, Project Glasswing update, May 2026
Remediation built for the AI era
Ahead of disclosure
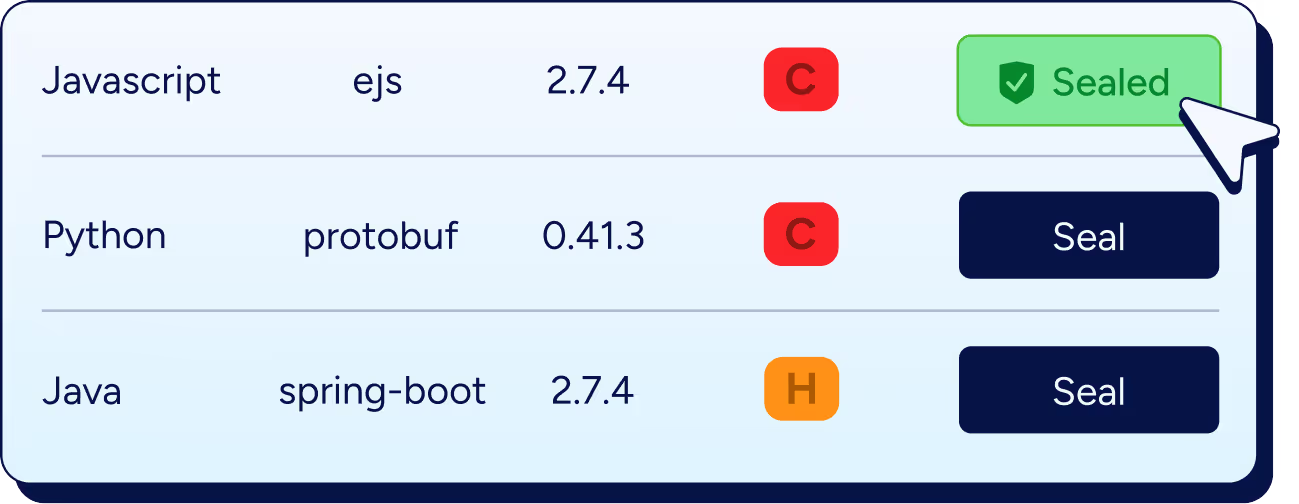
Fixed before the CVE goes public, and before a fixed version is released. Seal watches upstream code for security fixes that don't have a CVE yet, reproduces the vulnerability and ships a sealed version early. No upgrade required: patch now, upgrade on your own timeline. One CLI command, no manifest changes.
Verified, not generated
Seal stands behind every fix. Taken from the upstream fix and backported to your exact version. Built and tested against your version, reviewed by Seal's security engineers and validated by AI. Human-readable patches your team can review before applying.
Autonomous remediation. Human-approved.
Coding agents find the sealed version, create the Sealing Rule and request new fixes through the Seal MCP server. Every fix is visible, reviewable and approved by your team. Company-wide patching rules apply each fix to every affected project. No lock-in: sealed libraries stay in your registry, even if you stop using Seal.
Remediation your agents can run
Coding agents struggle with breaking upgrades, because a major-version migration needs judgment with input from multiple segmented services and undocumented tribal knowledge. A sealed version needs no migration, so an agent can apply it on its own. Through the Seal MCP server, agents in Claude Code, Cursor or any MCP-aware client can find the sealed version, create a Sealing Rule for every affected project and request a fix for anything not yet sealed, with the same permissions as the user.
Connect your agent
Fixes for every part of your stack

Secure application dependencies
Patch direct and transitive dependencies in place, even the ones your scanner marks as “unfixable”.
Uphold compliance and meet customer SLAs
Meet remediation deadlines for FedRAMP, PCI DSS 4.0, NYDFS, DORA and customer audits, even as finding volume grows.
Secure software nobody maintains anymore
End-of-life distros like CentOS and RHEL 6, abandoned libraries. If upstream stopped shipping fixes, Seal still does.
Secure containers and Linux infrastructure
Backported fixes across containers, base images, VMs and bare metal, without upgrading your OS.
Latest research and publications


Frequently asked questions
Discover how Seal Security identifies and patches open source vulnerabilities without breaking changes.